
Prevent scope creep by establishing a firm scope baseline and enforcing a formal change control process before work begins. This approach, grounded in PMI and PMBOK guidance, gives you the templates and tactics to catch unplanned work early and contain it when it slips through.
TL;DR:
- Maintaining an up-to-date scope baseline and controlling changes through a formal process prevents unapproved scope additions.
- Clear requirements, stakeholder sign-off, and a requirements traceability matrix are essential for early detection of scope creep patterns.
- Logging all requests, decisions, and impact assessments creates a documented record that discourages informal or unauthorized scope changes.
- Using short, frequent scope reviews, phased deliveries, and defined acceptance criteria helps keep scope aligned with project objectives.
- For ongoing projects, triaging requests and updating the baseline only after formal approval contain scope creep effectively.
Table of Contents
- What scope creep is and why it matters for projects
- Common causes and early warning signs of scope creep
- Core prevention framework: scope baseline, WBS, requirements traceability, and change control
- 7 practical tactics to prevent scope creep you can apply today
- How to stop or contain scope creep mid-project
- Templates, artifacts, and tool categories for repeatable prevention
- Author perspective: practical limits, diplomacy, and trade-offs
- Keeping client revisions from becoming scope creep with Audome
- FAQ
- Sources
What scope creep is and why it matters for projects
PMI defines scope creep, sometimes called requirement creep, as the uncontrolled expansion of project or product scope without corresponding adjustments to time, cost, or resources. It is one of the most commonly cited drivers of project failure, and it rarely arrives as one dramatic request. It accumulates through small additions that each seem reasonable in isolation.
The consequences compound quickly. Schedules slip because new work was never accounted for in the plan. Budgets run over because hours spent on unplanned features were never estimated or billed. Quality suffers when teams rush to absorb extra scope without extending deadlines. Stakeholders grow frustrated, either because delivery slips past promised dates or because the product that ships doesn’t match what they originally approved.
The distinction that matters here is between managed scope change and uncontrolled scope creep. Change itself is not the enemy. Projects evolve, markets shift, and new information surfaces. A managed scope change goes through documented review, cost and schedule impact analysis, and sponsor approval before it becomes real work. Scope creep skips that step entirely. It enters through side conversations, enthusiastic demo feedback, or a team member’s good intentions, and it never touches the baseline that was supposed to define the project’s boundaries.

Common causes and early warning signs of scope creep
Most scope creep traces back to a handful of recurring failures, and they tend to show up together rather than alone.
- Poorly defined requirements and vague acceptance criteria leave room for interpretation, and interpretation always expands rather than contracts.
- Shifting stakeholder priorities or the absence of a clear sponsor sign-off mean no one is accountable for saying no.
- Internal creep happens when the team itself adds polish, extra features, or “while we’re at it” improvements without approval.
- Weak or absent change control lets small requests bypass review because there’s no formal gate to stop them.
- Cumulative small requests are the most dangerous pattern: no single addition looks like a problem, but ten of them reshape the project.
The warning signs tend to appear before the damage does. Watch for a rising frequency of ad-hoc requests coming through email or chat instead of a formal channel. Informal agreements made in hallway conversations or quick calls, with no written record, are a near-certain predictor of later disputes over what was actually promised. One of the most common traps is what practitioners call the demo ambush: a stakeholder sees a work-in-progress demo, gets excited, and starts listing new features as if they were already agreed to. Mistaking that enthusiasm for formal acceptance is a well-documented error, and it’s worth training your team to recognize the difference between “I love this” and “yes, build this too.”
Core prevention framework: scope baseline, WBS, requirements traceability, and change control
The governance layer that actually stops scope creep rests on four connected pieces, and skipping any one of them weakens the other three.
-
Scope baseline. This is the approved scope statement, work breakdown structure, and WBS dictionary combined, and it serves as the formal reference point against which all scope performance gets measured. A scope baseline can only be changed through documented change control, never through a side conversation or an email thread. Once it’s approved, freeze it and version every subsequent revision so you can trace exactly what changed and when.
-
Work breakdown structure and WBS dictionary. The WBS decomposes deliverables into manageable, assignable pieces, but the dictionary is what makes it adjudicable. Each WBS entry should have a dictionary definition clear enough that anyone on the team can look at a new request and determine whether it fits inside an existing work package or falls outside it entirely.
-
Requirements traceability matrix. This document links every requirement to its source, owner, and test criteria, tracing it from business objective through implementation and testing. Traceability matrices are standard tools precisely because they make it hard for an undocumented feature to slip into a build unnoticed: if it isn’t in the matrix, it isn’t in scope.
-
Change control workflow. PMI’s guidance on Perform Integrated Change Control describes a process where every change request gets reviewed and managed centrally, with documented impact assessment before approval. The inputs include the change log, the traceability matrix, and the current baselines. A heavyweight version of this process is slow, but a lightweight one, built around a short checklist and a small change control board, can turn around most requests in a day or two without sacrificing rigor.
Treat the scope baseline as a living governance tool rather than a document you file away after kickoff. An outdated WBS dictionary quietly undermines the whole system, because the baseline stops being able to answer the one question it exists for: is this in scope? Practitioners who keep the dictionary current report that the baseline can resolve roughly 95% of day-to-day scope questions without escalation.
Pro Tip: Integrate your scope baseline with the schedule and cost baselines so every change request automatically triggers a time and budget impact check, not just a scope description.

7 practical tactics to prevent scope creep you can apply today
Governance documents only work if the team actually uses them day to day. These seven tactics turn the framework above into habits.
- Run a formal requirements workshop at project start and get written sign-off from the sponsor and key stakeholders before any work begins.
- Write deliverables and acceptance criteria in specific, testable language, and use a definition of done for every work package so “finished” isn’t a matter of opinion.
- Set a documented revision limit in the contract or statement of work, and spell out what happens, whether that’s additional cost or a formal change request, once that limit is reached.
- Schedule short, frequent scope pulse checks at each milestone rather than waiting for a quarterly review to discover the project has drifted.
- Break the project into phases or an MVP-first delivery so stakeholders prioritize what matters most now instead of requesting everything at once.
- Log every decision and every out-of-scope request in an auditable change log, even the ones you decline, so there’s a record if the conversation resurfaces later.
- Triage every incoming request into accept, decline, or defer, and attach a documented impact estimate to each decision before you communicate it.
Empirical research on scope creep found that it negatively correlates with project success, and that the root causes are consistently poor requirements gathering, weak stakeholder management, and the absence of change control procedures. In other words, the tactics above aren’t just good hygiene. They target the exact failure points the data points to.
How to stop or contain scope creep mid-project
When scope creep is already happening, the goal shifts from prevention to containment, and speed matters more than perfection.
- Triage the request immediately. Determine whether it’s a clarification of existing scope, a genuinely out-of-scope addition, or an emergency that threatens project viability. Each category gets a different response path.
- Record hours and costs separately from the moment you suspect creep, so you have evidence of actual impact rather than a rough guess when the conversation with the sponsor happens.
- Assemble a change-request package that spells out the cost impact, schedule impact, and any new risks, so the sponsor is deciding based on facts, not vibes.
- Negotiate trade-offs using your prioritized backlog: if the new item matters enough to add, something else likely needs to move out or get deferred.
- Update the baseline and communicate the change if approved, or document the decision and re-plan around it if rejected, so the record stays accurate either way.
Small, seemingly benign additions often carry hidden interdependent risk, touching integration points, QA coverage, or downstream tasks that weren’t obvious at first glance. A change-request checklist that forces you to name those dependencies before approval prevents the kind of optimistic, parallel-tasking planning that looks fine on paper and falls apart in execution.
Pro Tip: Never let a verbal “sure, that’s fine” substitute for an updated baseline. If it isn’t written down and versioned, it isn’t approved.
Templates, artifacts, and tool categories for repeatable prevention
A handful of reusable artifacts turn scope prevention from a one-time effort into a repeatable system.
- A scope statement template should force you to list deliverables, explicit exclusions, acceptance criteria, and underlying assumptions, since exclusions are often what gets argued over later.
- Your WBS and WBS dictionary need enough detail that any work package can be assigned, estimated, and checked for completion without further explanation, but not so much detail that maintaining it becomes its own project.
- A change-request checklist and a short change control board agenda should cover cost impact, schedule impact, risk, and sponsor decision, with a clear owner for each field.
- A requirements traceability matrix needs at minimum an ID, source, owner, linked test case, and current status for every requirement.
- For tooling, look at change-log trackers, traceability spreadsheets, and versioned artifact repositories that keep a clear history of what changed and when; a copyable one-page scope statement and two-level WBS is a useful starting template if you’re building these from scratch.
Author perspective: practical limits, diplomacy, and trade-offs
Enforcing a change control process will occasionally feel like friction with people you need on your side, and the skill isn’t saying no, it’s saying “here’s the cost, do you still want it.” Escalate when a request threatens the baseline’s integrity, not every time someone asks a question. Some scope changes genuinely improve the outcome and deserve a yes; the discipline is making sure that yes goes through the same documented path as everything else, so it never becomes an exception that swallows the rule.
— Kreg
Keeping client revisions from becoming scope creep with Audome
Audio and media projects face a version of scope creep that looks a little different: endless revision rounds, feedback scattered across email and text threads, and clients who keep asking for “one more small change” long after the brief was approved. We built Audome to give studios the same kind of boundary that a change-control process gives a software project, but sized for the way producers and engineers actually work with clients.
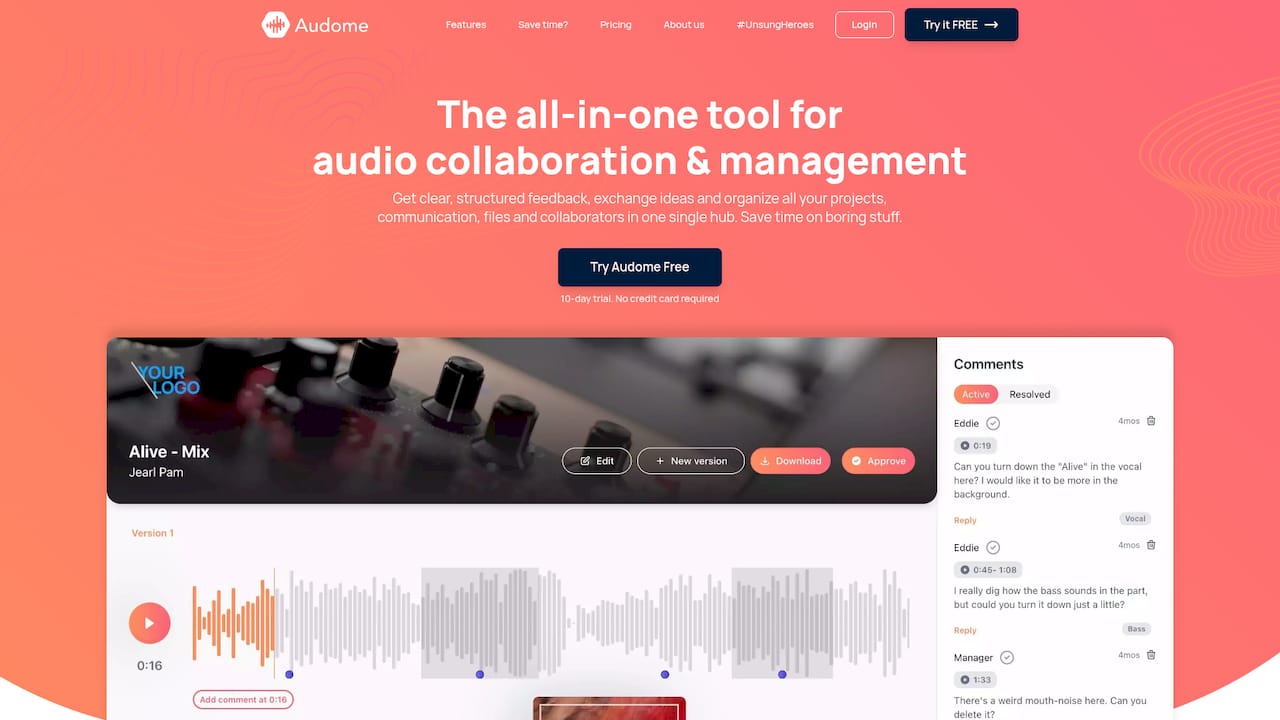
- Timestamped feedback directly on the waveform helps replace scattered comments across email, Discord, and text messages, so every request can be tied to an exact moment in the file.
- Version history tracks revisions automatically, giving a record of what changed and when without manually renaming files.
- Revision limits let you cap the number of free rounds included in a project and provide options to charge for extras, turning an open-ended revision cycle into a defined scope.
- Integrated payments require payment before final downloads unlock, so delivery stays tied to a completed, paid engagement.
Pair these with the practices in our guides on resolving client comments in one edit pass and setting revision limits for producers and you have a working version of the scope baseline and change control model built specifically for audio work. See Audome pricing to find a plan that fits your studio.
FAQ
How do we avoid scope creep?
Avoid scope creep by locking a documented scope baseline before work starts and routing every proposed change through a formal change control process rather than informal agreement. Combine that with a requirements traceability matrix so undocumented features cannot quietly enter the build.
What are the strategies for scope creep?
The core strategies are defining scope clearly upfront, securing stakeholder sign-off, running continuous monitoring through milestone checks, and maintaining a documented change process for anything new. A commonly repeated seven-point approach also includes setting clear goals, communicating regularly, and favoring MVP-style delivery to limit how much scope stakeholders request at once.
How to counter scope creep?
Counter scope creep by triaging each incoming request as a clarification, an out-of-scope addition, or an emergency, then documenting its cost and schedule impact before any decision gets made. Update your baseline only after formal approval, and log declined or deferred requests so the record stays complete.
Which action is important to perform to avoid scope creep?
The single most important action is establishing and freezing a scope baseline, since it’s the reference point every future request gets measured against. Without it, there is no clear boundary to defend, which makes uncontrolled scope expansion far more likely.
Sources
For primary guidance, see PMI’s work on integrated change control and scope baselines, plus empirical research on how scope creep affects project outcomes.
- Scope Baseline in PMBOK 8 — Complete Guide
- PMBOK Guide — Perform integrated change control (PMI)
- The impact of scope creep on project success: an empirical investigation — Zenodo (2022)